
Bitcoin Correlation With Stocks: S&P 500 & Nasdaq Data


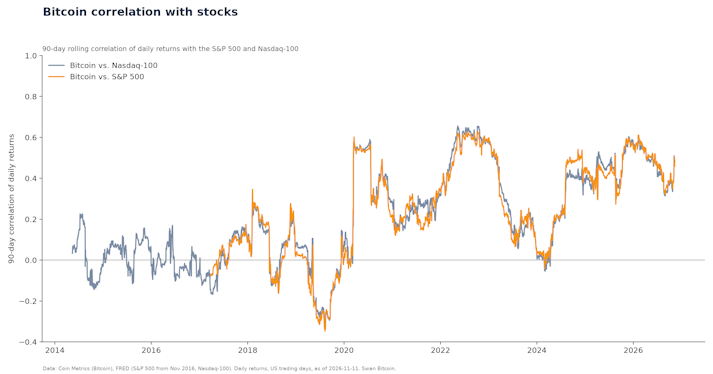
Bitcoin’s correlation with the S&P 500 was 0.42 in 2025 and 0.46 over the last 90 days (Nov 2026). Yearly data since 2017, Nasdaq, dollar and crash days.
In this article
The Byzantine Generals Problem is the challenge of getting a group to agree on one plan when some members may lie and no one can tell which messages to trust. Computer scientists Leslie Lamport, Robert Shostak and Marshall Pease named it in a 1982 paper. In November 2008, Satoshi Nakamoto wrote that “the proof-of-work chain is a solution to the Byzantine Generals' Problem,” and Bitcoin has applied that solution to every block since the network launched in January 2009.
Why should you care? Because the problem is really about money. Any money that no central authority controls needs a way for strangers to agree on who owns what, even when some of them are cheating. That is what centralized financial systems solve with trusted middlemen, and it is what Bitcoin solves without them:
The 2008 financial crisis showed what that trust can cost: large banks received bailouts while the public paid the price.
Central banks that print money to stimulate the economy leave it debased and devalued over time.
A peer-to-peer electronic cash system that needs no trusted third party avoids both problems, but only if it solves the Byzantine Generals Problem.
The Byzantine Generals Problem is a thought experiment about reaching agreement in a distributed system, where many computers (nodes) must agree on the same data even if some of them are faulty or dishonest.
Swan Bitcoin
Here’s the scenario from the 1982 paper:
Several divisions of the Byzantine army surround an enemy city. Each division has its own general, and the generals can only communicate by messenger.
If they all attack at the same time, they win. If they attack at different times, they lose. So they need to agree on one plan.
Some generals are traitors. The traitors will send conflicting messages to sabotage the plan, and the loyal generals can’t tell which messages are false.
The question: how can the loyal generals reach the same decision anyway?
The paper’s answer is precise. With ordinary spoken messages, the problem is “solvable if and only if more than two-thirds of the generals are loyal; so a single traitor can confound two loyal generals.” With unforgeable signed messages, it is solvable for any number of traitors. The paper was published in ACM Transactions on Programming Languages and Systems in July 1982 (Microsoft Research).
The name refers to the Byzantine Empire, whose capital, Constantinople, is today’s Istanbul.
The Two Generals' Problem is the simpler version: two loyal generals, no traitors, but any messenger might be captured. It was the first computer communication problem proven to be unsolvable. The Byzantine version adds the harder part: participants who actively lie.
A system is Byzantine fault tolerant (BFT) if it keeps working correctly even when some of its parts fail or act maliciously. The 1982 result sets the bar for classical systems: with ordinary messages, at least 3m + 1 participants are needed to cope with m traitors, so fewer than one-third can be faulty. Those classical systems also need a known, fixed list of participants.
Bitcoin had to work without that list. Anyone can join or leave the network at any time, under any name. That is why the earlier approaches couldn’t produce open, decentralized money, and why proof-of-work was the breakthrough.
Commodity money had limits. Metals, shells and beads have all served as money. Gold earned the most trust, but it is heavy, hard to verify and hard to move (the limits of gold).
Central control replaced it. Nation-states took over money to make it easier to trust, and history shows they often break that trust.
Decentralized digital money kept failing. Many tried to build money that works independently of governments, but none could stop participants from cheating without a central referee.
Bitcoin solved it. Satoshi published the Bitcoin white paper on October 31, 2008, and the network went live in January 2009, with no central party deciding which transactions are valid (the mysteries of Bitcoin).
Satoshi explained the motivation when announcing Bitcoin on the P2P Foundation forum on February 11, 2009 (see also how Bitcoin solves the fundamental problem of money):
“The root problem with conventional currency is all the trust that’s required to make it work. The central bank must be trusted not to debase the currency, but the history of fiat currencies is full of breaches of that trust.”
-Satoshi Nakamoto, the creator of Bitcoin
Bitcoin solves it with proof-of-work and a shared ledger, the blockchain. Every participant accepts the valid chain with the most accumulated work as the true history, and producing that work costs real energy, so lying is expensive and easy to spot.
Satoshi explained it in the generals' own terms in an email on November 13, 2008. In his version, any general can announce an attack time, and each general starts on a hard proof-of-work puzzle that includes the first time he heard. When one finds a solution, he broadcasts it and everyone builds on it. “If anyone was working on a different attack time, they switch to this one, because its proof-of-work chain is now longer.” After two hours, one attack time is backed by a chain of 12 proofs-of-work, and every general can see that most of the army worked on it. As Satoshi put it: “The proof-of-work chain is how all the synchronisation, distributed database and global view problems you’ve asked about are solved.”
In Bitcoin today, the parts map like this:
Generals → nodes and miners. Nodes check every block and transaction against the rules. Miners compete to add the next block.
Messages → blocks of transactions. A block only counts if it carries a valid proof-of-work, which takes hash power and electricity to produce.
The agreed plan → the blockchain. Every node follows the valid chain with the most accumulated work, so all honest nodes end up with the same history of who owns what.
Traitors → invalid blocks. A block that breaks the rules, such as one that spends coins twice, is rejected by every node, no matter how much hash power produced it.
Geeks For Geeks
The Bitcoin white paper states the security assumption plainly: “As long as a majority of CPU power is controlled by nodes that are not cooperating to attack the network, they’ll generate the longest chain and outpace attackers.”
That majority is large. As of November 11, 2026, the network’s hashrate averaged about 951 exahashes per second over the previous week, at a mining difficulty of 148.36 trillion and a block height of 975,472 (mempool.space). Rewriting Bitcoin’s history would mean out-spending all of that honest mining, which is why the cost of mining is also the cost of attacking it.
immutable — in the context of a blockchain, implies that the data or ledger is permanent and tamper-proof, and its history cannot be modified or changed after its creation
Because every node verifies everything independently, Bitcoin is a trustless system in which all participants can agree on a single truth. For a step-by-step look at the machinery, see how Bitcoin actually works.
Wikipedia
Wikipedia’s article on Byzantine faults cites this guide in its section on Bitcoin and proof-of-work (still listed as of November 11, 2026).
Proof-of-work makes cheating expensive, but someone still has to run the nodes. In November 2008, early Bitcoin contributor Hal Finney listed scenarios in which the network could keep running. One of them:
Satoshi Nakamoto Institute
Satoshi replied on November 14, 2008: “It’s very attractive to the libertarian viewpoint if we can explain it properly. I’m better with code than with words though.”
In practice, both incentives matter. Miners earn new Bitcoin and fees only if their blocks follow the rules, and people run their own nodes to verify their transactions instead of trusting anyone else’s.
Because Bitcoin solved the Byzantine Generals Problem, you can hold money whose supply and ownership no bank or government can quietly change. No central party decides which transactions count. Every rule is checked by everyone, and the history is protected by all the work honest miners have done. That is the alternative to a banking system in which a central authority decides for everyone, and to the Cantillon Effect, where new money benefits those closest to it first. New to the topic? Start with what Bitcoin is.
Hold your IRA with the most trusted name in Bitcoin.
It is the problem of getting a group to agree on one decision when some members may lie and messages can’t be trusted. In computing, it describes how a network of computers can agree on the same data when some of them are faulty or malicious.
Leslie Lamport, Robert Shostak and Marshall Pease, in a paper titled “The Byzantine Generals Problem,” published in ACM Transactions on Programming Languages and Systems in July 1982.
With proof-of-work. Miners spend real computing power to add each block, and every node follows the valid chain with the most accumulated work. Nodes reject invalid blocks, so dishonest participants can’t change the rules, and rewriting history would require more computing power than all honest miners combined.
Yes, as long as honest participants control the majority of the network’s computing power. The white paper says honest nodes will “generate the longest chain and outpace attackers” under that condition.
The Two Generals Problem has two loyal parties and an unreliable messenger, and it has been proven unsolvable. The Byzantine Generals Problem adds traitors who send false messages on purpose.
The 1982 paper describes generals of the Byzantine army surrounding an enemy city. The Byzantine Empire’s capital was Constantinople, today’s Istanbul.
Lamport, Shostak and Pease, The Byzantine Generals Problem, ACM Transactions on Programming Languages and Systems, July 1982
Satoshi Nakamoto, Bitcoin: A Peer-to-Peer Electronic Cash System (October 31, 2008)
Satoshi Nakamoto Institute, emails of November 13, 2008 and November 14, 2008, and the P2P Foundation post of February 11, 2009
mempool.space, hashrate and difficulty (checked November 11, 2026)
Wikipedia, Byzantine fault and Two Generals' Problem
Matt Ruby is a seasoned content writer helping educate million worldwide about Bitcoin for Swan. Matt work with tech companies to create words, videos, and other content that makes them seem human. He specializes in taking boring/drab tech topics and making them interesting, educational, funny, and accessible to regular people.
Thoughts on Bitcoin from the Swan team and friends.
Bitcoin’s correlation with the S&P 500 was 0.42 in 2025 and 0.46 over the last 90 days (Nov 2026). Yearly data since 2017, Nasdaq, dollar and crash days.
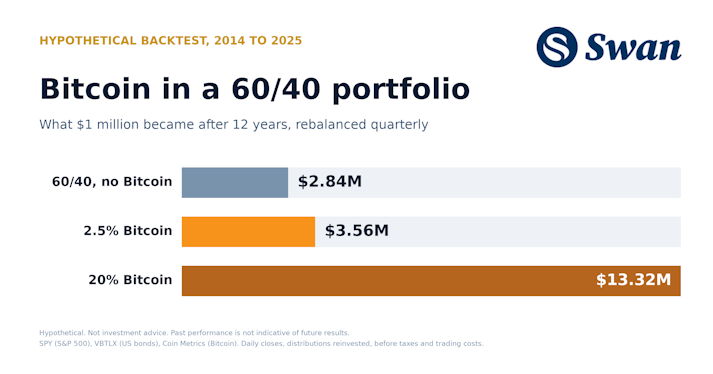
How much Bitcoin to hold in a 60/40 portfolio: 2.5% lifted annual returns from 9.1% to 11.2% (2014–2025). Results from 1% to 20%, drawdowns and method.
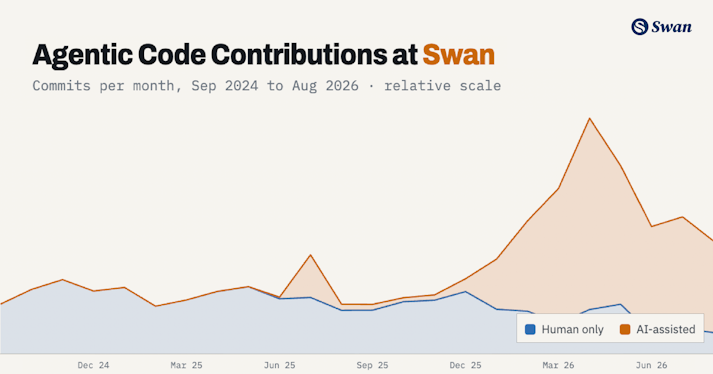
How Swan built an agentic software factory that finds production bugs, reaches consensus on the fix, opens the PR, and proves it works before a human merges.